DORA training: what Articles 13 and 5 require
DORA training is an obligation under Regulation (EU) 2022/2554. Financial entities must offer all their staff, management included, ICT security awareness programs. They must add training in digital operational resilience. The text speaks of mandatory modules, without imposing a format. An annual e-learning can therefore be part of it, but it is not the only answer.
DORA is a European regulation, relevant to US financial groups operating in the EU. Here is what Articles 13 and 5 provide, who is covered, and how to build a program that changes reflexes.
What DORA requires: Article 13, paragraph 6
DORA has applied since January 17, 2025, directly in all Member States, without a transposition law. Article 13, paragraph 6, requires financial entities to develop these awareness programs and this training. They must include them in their staff training plans as mandatory modules.
These programs target all employees and members of management. The level of complexity must be proportionate to their functions. The text sets no frequency, duration or medium.
ICT third-party service providers may also be concerned “where appropriate”. This depends on the conditions laid down in the contracts (Article 30, paragraph 2, point i).
Who is covered by DORA training
The scope is in Article 2 of the Regulation. It covers in particular credit and payment institutions, investment firms and insurers. It also targets insurance intermediaries and crypto-asset service providers. The full list is available on EUR-Lex.
The simplified regime in Article 16 repeats the same requirement. It also asks for awareness and training programs for staff and management. Smaller entities are therefore not exempt.
Management training: Article 5
Article 5, paragraph 4, targets the management body. Its members must actively keep up to date sufficient knowledge and skills to understand and assess ICT risk. They must regularly follow specific training, proportionate to that risk.
Article 5, paragraph 2, also makes the management body responsible for the budget. It must allocate resources to the awareness programs and training referred to in Article 13, paragraph 6, and review them periodically. Training is therefore not only a matter for the training department: it is a governance issue.
What the text does not say, and what supervisors expect
DORA does not define what “sufficient” training is. In its questions-and-answers database, EIOPA (the European insurance authority) indicates that this training must be adapted to the functions of staff and management. The reading is therefore proportionate: a board member, a branch advisor and a system administrator do not have the same needs.
Delegated Regulation (EU) 2024/1774 specifies the ICT risk management framework. It adds that staff must know the channels for reporting anomalous behavior. Knowing who to escalate an alert to is therefore part of the training.
In France, the ACPR, the French prudential supervisor, published a DORA notice on ICT in December 2024 and an ICT annex to the internal control report. An institution should expect to have to explain its program, its audience and its assessments.
Why annual e-learning does not settle the human risk
A module on passwords and suspicious links passes on information. It does not prepare for the call from a fake advisor, a fake provider or a fake support coworker. That person presses the employee to obtain a code or an approval.
In these situations, the caller is polite, well informed and in a hurry. The employee must find words to verify, refuse and report, often within seconds. This reflex is built by practicing it. Our article on the limits of e-learning for cybersecurity reflexes explains the mechanism.
DORA asks for training in digital operational resilience, not a certificate of reading. A program that does not change what people do on the day of an attack meets the letter of the text, not its objective.
A typical scenario for a back-office team
Imagine a call received by a payments administrator. The caller introduces himself as a technician from one of the bank's IT providers. He explains that an incident is blocking transfers and asks, to resolve it, for a code received by text message on the administrator's phone.
The scenario tests three actions: verifying identity through an independent channel, refusing to share the code, reporting the call. The useful phrases are short:
- “I never share a code by phone. I will call you back on the number in the contract.”
- “Give me your name and department, I am noting them and I will alert security.”
- “If it is urgent, the incident will be opened through the usual process.”
These actions appear in our articles on refusing under pressure on the phone and on the callback. They are part of operational resilience: an incident avoided is better than an incident well handled.
Common mistakes in DORA programs
- Forgetting management. It is targeted twice, in Articles 5 and 13.
- Treating training as a mere paper trail. The text speaks of resilience, therefore of behaviors.
- Identical content for everyone. Proportionality to functions is in the text.
- Training only in writing. Phone attacks are not prepared for with texts alone.
- Not reviewing the program. The management body must review it periodically.
Building a DORA program that works
- Segment the audiences. Management, advisors and front office, back office and treasury, IT teams, support. Each group receives the situations that concern it.
- Combine formats. Short modules for basic knowledge, practice sessions for sensitive actions.
- Train orally. Phone attacks play out in conversation. Role-play is the right format to answer them.
- Debrief and replay. Precise feedback on what was said, then a new attempt.
- Keep records. Who, when, on what, with what assessment, including for management.
A five-question grid to audit your program
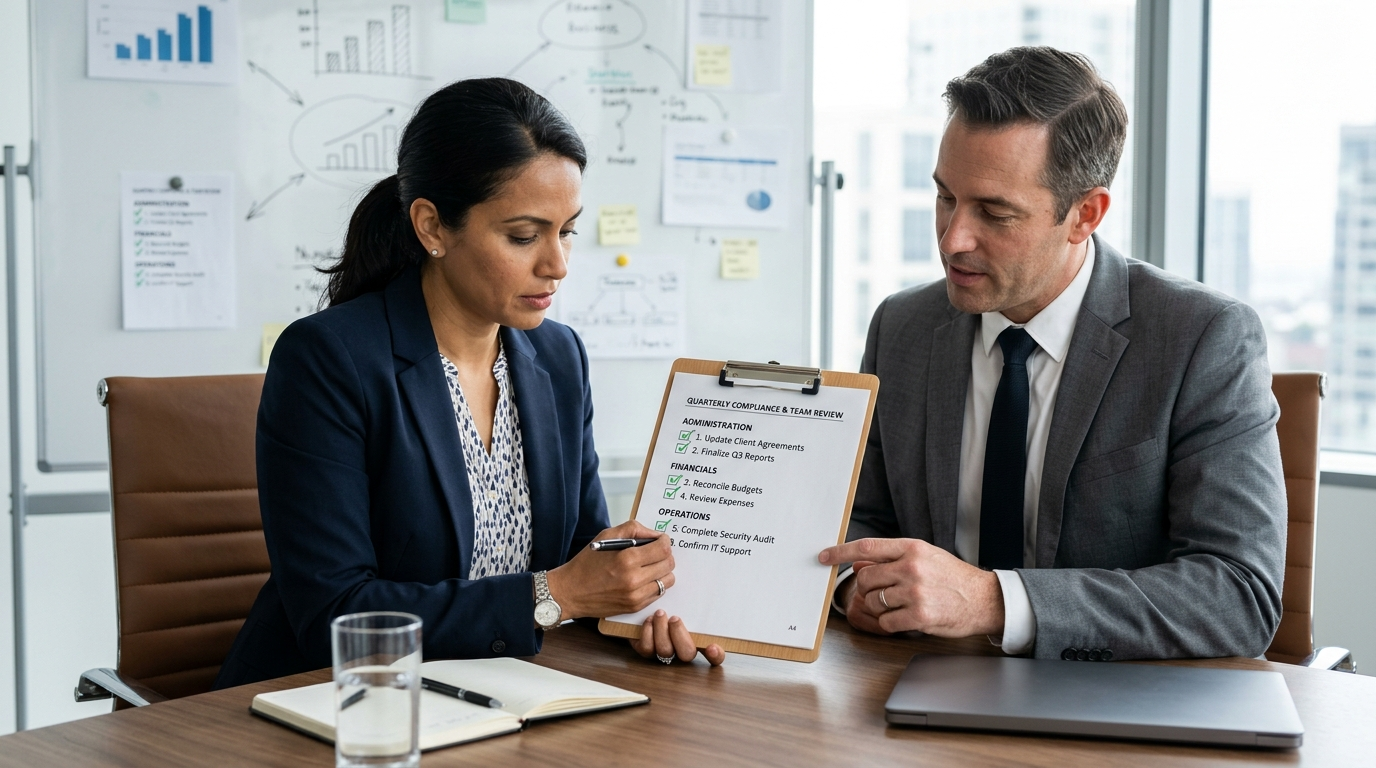
- Are all employees and all members of management covered?
- Is the content adapted to each function?
- Are the modules mandatory, as the text requires?
- Does staff know who to report an incident to?
- Can you prove what has been learned, and not only what has been opened?
Role-play, a way to meet the obligation
Face Up lets trainers create their own role-plays from their real cases, with the help of a design assistant. The learner speaks, by voice or on video, with a persona played by an AI. It could be a fake bank advisor or a fake IT provider.
They then receive a debrief: strengths, points to improve, action plan and quotes of what they said. They can replay. For the banking sector, we detail the scenarios in our article on vishing in banks. The question of evidence is covered in the article on training traceability.
Frequently asked questions
Does DORA impose a number of training hours?
No. Article 13, paragraph 6, speaks of programs and mandatory modules, with no figure for duration or frequency. The level must be proportionate to the functions of the people trained.
Should executives also be trained?
Yes, in two ways. They are targeted by Article 13 like all members of management. Article 5 also requires the management body to regularly follow training specific to ICT risk.
Are ICT service providers covered?
They may be. Article 13 mentions third-party providers “where appropriate”. Article 30 provides that contracts may require them to follow the entity's programs.
Is e-learning enough to be compliant?
The text prohibits no format. In practice, an entity will have to show that its program is adapted to functions and addresses real risks. A uniform module shows this poorly.
To move from certificate to practice, start with the teams most exposed by phone, then extend the program. Our overview of mandatory training places DORA among the other obligations, and the article on management training under NIS2 gives its European counterpart. To see a role-play on one of your cases, book a demo.
From reading to practice.
Pick a real-life situation and talk to an AI persona, by video with an avatar or by audio call. 5 to 10 minutes, no account, instant debrief.
Try a scenario →